Why Enterprises Cannot Afford to Ignore It
For an enterprise, a security incident is never just a technical problem. It can mean regulatory penalties, service downtime, lost customer trust, and weeks of recovery work. Because enterprises run many applications and handle large volumes of sensitive data, strong multi-cloud security protects more than systems. It protects revenue, reputation, and the confidence of customers and partners. Investing in it early is almost always cheaper than reacting after something goes wrong.
What Is Multi-Cloud Security?
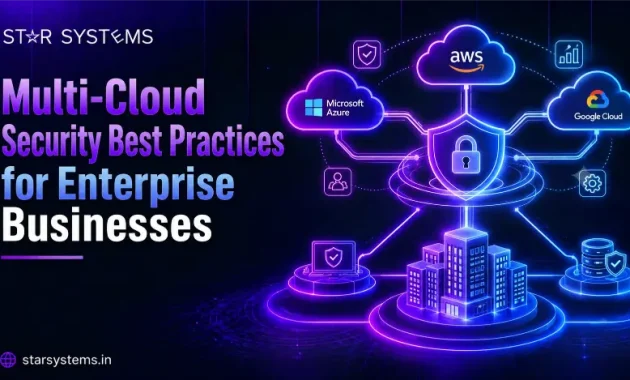
Multi-cloud security is the set of policies, tools, and habits that protect an organization’s data and applications across more than one cloud provider. The goal is simple: apply the same level of protection everywhere, no matter which platform a workload runs on.
Why Is Multi-Cloud Security Harder?
- Inconsistent settings: A rule that is strict on one platform may be missing on another.
- Limited visibility: Separate dashboards make it hard to see the full picture.
- A larger attack surface: More accounts, connections, and users mean more entry points.
- Complex compliance: Regulations may apply differently across regions and providers.
- Skills gaps: Few teams are expert in every platform.
10 Multi-Cloud Security Best Practices
1. Understand the Shared Responsibility Model
Cloud providers secure the underlying infrastructure. You are responsible for your data, access, and configurations. Document who owns what on every platform.
2. Centralize Identity and Access Management
Use one identity system with single sign-on and multi-factor authentication. Apply least privilege, so people only get the access their role needs.
3. Adopt a Zero Trust Approach
Never trust a user or device by default. Verify every request, and limit access to only what is required.
4. Encrypt Data Everywhere
Encrypt data at rest and in transit across all clouds, and manage encryption keys carefully with clear ownership and rotation rules.
5. Standardize Security Policies
Define one security baseline and enforce it across providers. Using infrastructure as code helps keep configurations consistent and repeatable.
6. Scan for Misconfigurations Continuously
Cloud security posture management (CSPM) tools automatically detect risky settings, such as open storage or overly broad permissions, so teams can fix them quickly.
7. Centralize Logging and Monitoring
Collect logs from every cloud into one place. A central view makes unusual activity far easier to spot and investigate.
8. Secure Your Network
Segment networks, restrict traffic to what is needed, and use private connections between environments instead of exposing services to the internet.
9. Automate Compliance and Governance
Use consistent tagging, automated policy checks, and regular audits to prove compliance and catch drift early.
10. Plan and Test Incident Response
Create a response plan that covers every provider, keep tested backups, and run practice drills so your team knows exactly what to do under pressure.
Common Risks and the Practice That Fixes Them
Who Owns Multi-Cloud Security in an Enterprise?
In large organizations, security fails most often when everyone assumes someone else is responsible. A simple structure works well. A central security team sets the standards and monitors results. Cloud platform and DevOps teams apply those standards in their daily work. Compliance and risk teams check that rules are followed, and business owners approve access to the data they are accountable for. Clear ownership turns enterprise cloud security from a vague goal into a weekly routine.
A Practical Starting Plan for Enterprises
- Take inventory: List every cloud account, workload, and data location across all providers.
- Set your baseline: Agree on one security standard for identity, encryption, networking, and logging.
- Fix the biggest gaps first: Start with public exposure, weak access controls, and unencrypted data.
- Automate checks: Add posture scanning and policy enforcement so problems are caught as they appear.
- Review and practice: Run regular audits and incident drills, then update your standard as you learn.
Common Mistakes to Avoid
- Assuming each provider’s default settings are secure enough.
- Managing security separately on each platform, with no shared standard.
- Giving broad permissions “temporarily” and never removing them.
- Treating security as something to add after the migration is finished.
How Star Systems Helps Secure Multi-Cloud Migration
Migration is one of the riskiest moments for security, because workloads, networks, and permissions all change at once. Our Infra Bridge migration platform supports secure moves from AWS, Azure, Google Cloud, IBM Cloud Classic, or on-premises environments into IBM Cloud VPC. It uses a read-only discovery process that does not alter your source systems, and it recreates active firewall rules as native VPC security groups and network access control lists. Combined with our cloud migration services, security is planned from the first assessment, not added at the end.
Key Takeaways
- Consistency across providers matters more than any single tool.
- Identity is the new perimeter, so centralize it and apply least privilege.
- Automate scanning and compliance to catch problems early.
- Plan security before migration, not after.
Want a clear view of your multi-cloud security risks? Talk to Star Systems for a free assessment and a practical roadmap.